Packet Analyzer
The problem
I wanted to understand live network traffic hands-on, without the weight of a full GUI analyzer.
What I built
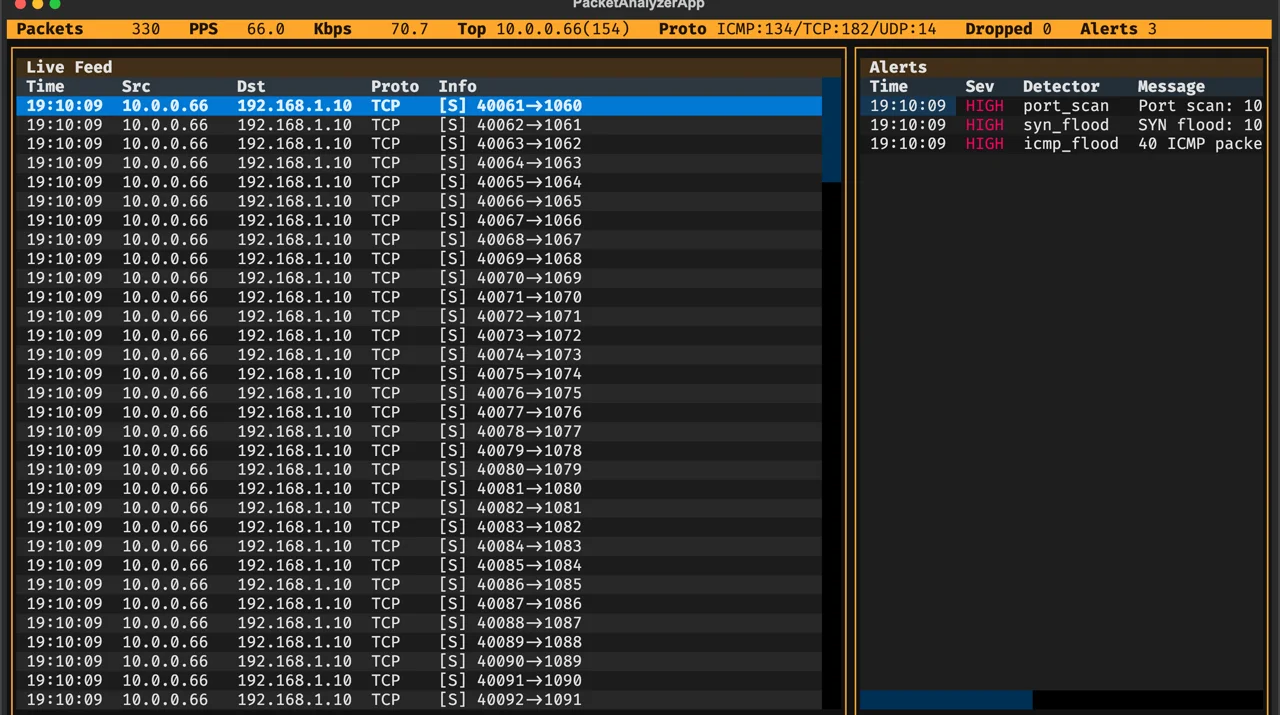
A terminal packet sniffer: Scapy captures traffic on a producer thread, a bounded queue feeds a Textual TUI at 5 Hz, and five real-time detectors (SYN flood, ICMP flood, port scan, DNS anomalies, traffic spikes) flag unusual patterns; PCAP import/export included.
The result
A Wireshark-lite you can run in any terminal. Replaying synthetic attacks found two defects unit tests had missed: a distributed SYN flood produced zero alerts under per-source counting, and every detector leaked state on one-shot keys. Both fixed with regression tests; 31 tests, CI on Python 3.10–3.13.